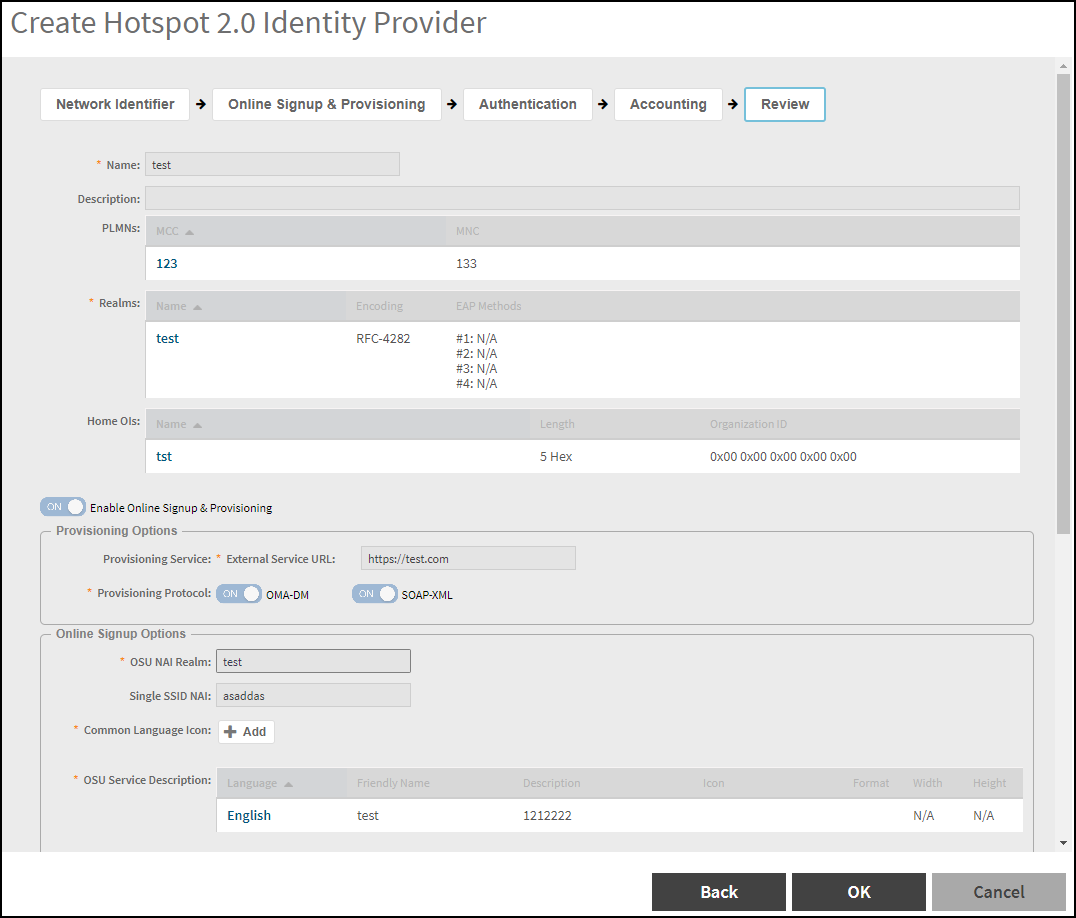
Creating a Hotspot 2.0 Identity Provider
Configure the Hotspot 2.0 Identity Provider
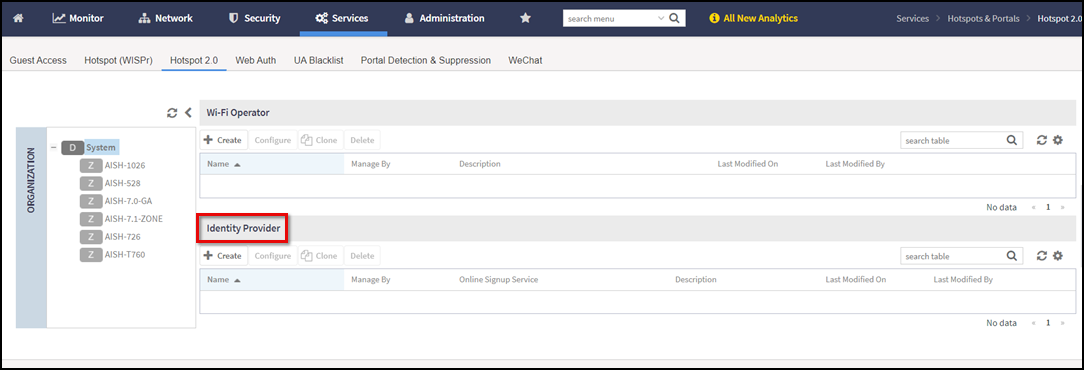
- On the menu, click to display the Identity Provider window.
- In the Organization tab, select the zone for which you want to create the Identity Provider portal.
- In the Identity Provider tab, click Create to open the Create Hotspot 2.0 Identity Provider page.
- Configure the following sections to create a Hotspot 2.0 Identity Provider:
Network Identifier
- Complete the
following fields:
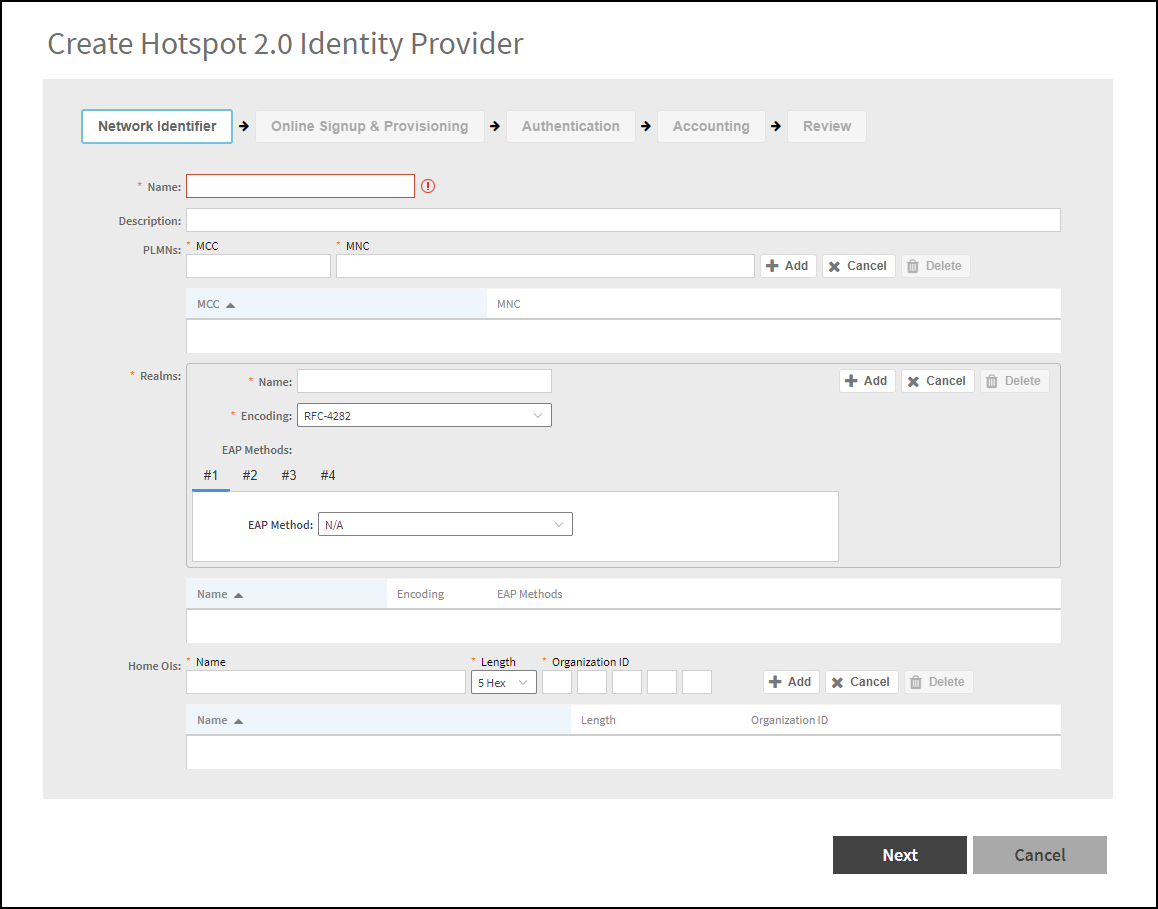
- Name: Enter a name or this network identifier profile.
- Description: Enter a description for the network identifier profile.
- PLMNs: Each record contains MCC and
MNC.
Complete the following fields and click Add to add the PLMNs. The configured information will be displayed in a table below the PLMNs field.
- MCC: Set the correct country code for the geographical location. This is required when the controller sends MAP authentication information. Type the mobile country code digits. Decimal digit strings with maximum length of 3 and minimum length of 2.
- MNC: Set the mobile network code based on the geographical location. This is required when controller sends MAP authentication information. Type the mobile network code digits. Decimal digit strings with maximum length of 3 and minimum length of 2.
- Realms: List of NAI realms
corresponding to service providers or other entities whose networks or services are
accessible via this AP. Up to 16 NAI realm entries can be created. Each NAI realm
entry can contain up to four EAP methods.
Complete the following fields and click Add to add the Realms. The configured information will be displayed in a table below the Realms field.
- Home Ols: Organization Identifier
(OI) is a unique value assigned to the organization. User can configure a maximum
of
12 OI values and can adjust the order since the AP takes only 3 OIs in the beacon.
Complete the following fields and click Add to add the Home Ols. The configured information will be displayed in a table below the Home Ols field.
- Click Next.
Online Signup and Provisioning
- Complete the following fields:
- Provisioning Options tab, complete
the following fields:
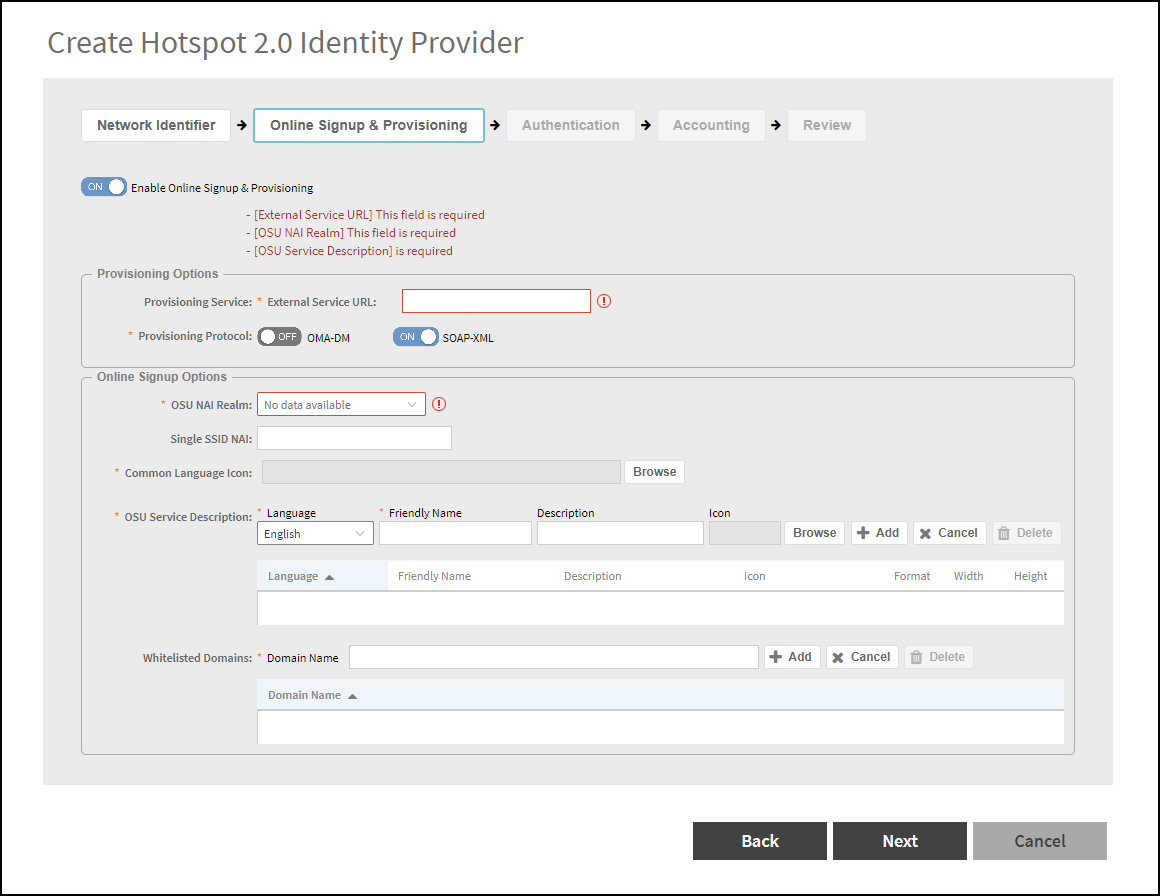
- Provisioning Service.
External Service URL: Enter the external OSU server URL.
The provisioning service is responsible for any subscription provisioning process in which messages are communicated between the UE and the SZ resulting in a PPS-MO provisioned into the UE. The provisioning supports both SOAP-XML and OMA-DM as communication protocols for the process based on the initial request coming from the UE. The provisioning service supports sign-up; remediation and policy update flows where the UE is provisioned with a full PPS -MO or only with internal node/s of the PPS-MO. Administrator can only set External Internal Provisioning Services, where the administrator is required to fill the external OSU server URL.
- Provisioning Protocol: Switch ON communication protocols OMA-DM or SOAP-XML.
- Provisioning Service.
- Online Signup Options tab, complete
the following fields:
- OSU NAI Realm: Select from the
drop down list.
This configuration is only for External Provision Service. In case of Internal Provisioning Service, the NAI realm should be configured per authentication service, which is available during on-boarding.
- Single SSID NAI: Enter the
SSID.
This configuration is for enabling single SSID for WLAN profile, The NAI length can have a maximum of 255 charecters.
- Common Language Icon: Click
Browse
to upload the language icon.
This is the default icon presented in the device for this identity provider in case the device does not find any match for other icons per language in the table.
Please can you explain more about this feature. - OSU Service Description: This
configures the friendly name, description and icon per language. This
information is presented on the device when it receives ANQP message which
includes OSU providers. Friendly names, which are required to be part of the OSU
certificate is automatically populated in this table. In case description is
also included in the OSU certificate it is automatically populated into the
table. Administrators are required to set the matched icon per language as
included in the OSU certificate.
Complete the following fields and click Add to add the OSU Service Description. The configured information will be displayed in a table below the OSU Service Description field.
- Language: Select the language from the drop down list.
- Friendly Name: Enter the name.
- Description: Enter the description.
- Icon: Click Browse to upload the icon.
Click Cancel to exit from the creating OSU Service Description. To delete the OSU Service Description, select the Friendly Name and click Delete .
- Whitelisted Domain: Add the domain names and click Add to add the External Portal domain.
- OSU NAI Realm: Select from the
drop down list.
- Provisioning Options tab, complete
the following fields:
- Click Next.
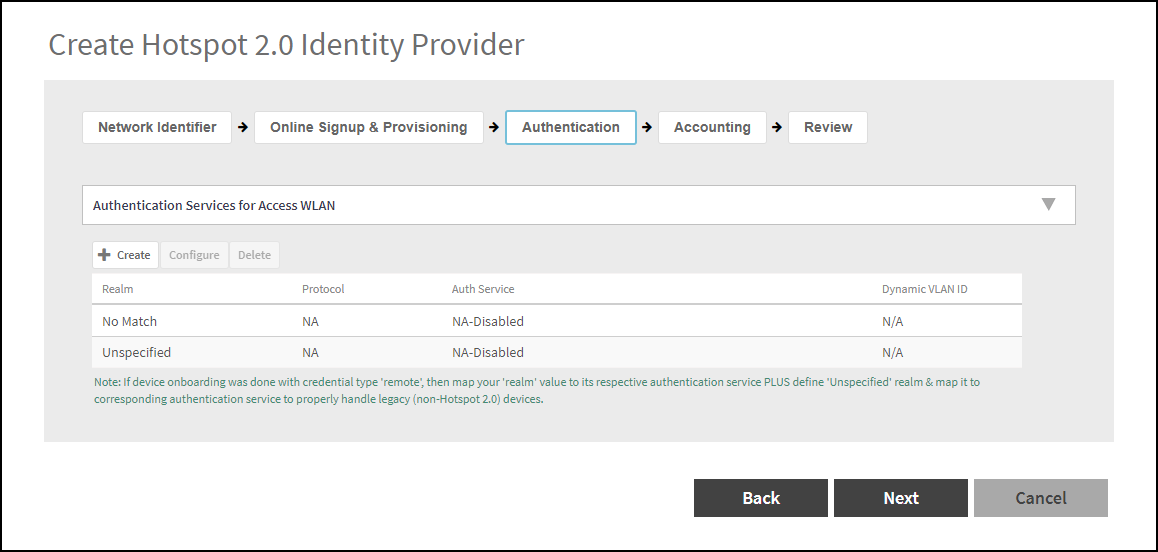
Authentication
- Complete the following fields:
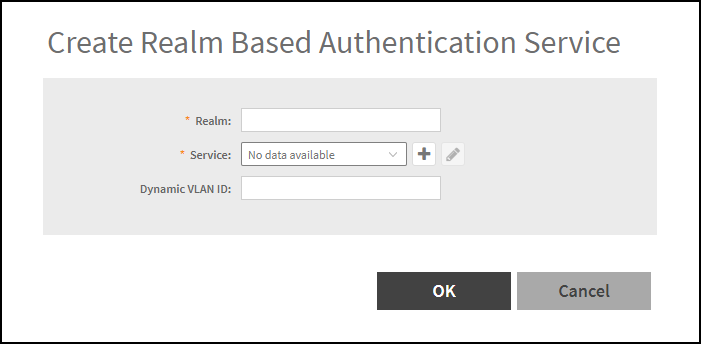
The Create Realm Based Authentication Sevice page is displayed.
Complete the following fields:
- Realm: Enter the realm information to configure the realm mapping to the authentication service.
- Service: Select the service from
the drop down list to map the realm to an external RADIUS server which should be
pre-configured.
To create a realm service, click the
 icon to display the Create Authentication
Service dialog box. Create an authentication service, refer to Creating Realm Based Authentication Profile.
- Dynamic VLAN ID: Enter the VLAN ID.
To modify the realm, select the realm from the table and click Configure icon.
To delete the realm, select the realm from the table and click Delete icon.
- Click Next.
 icon
to edit the selected realm service.
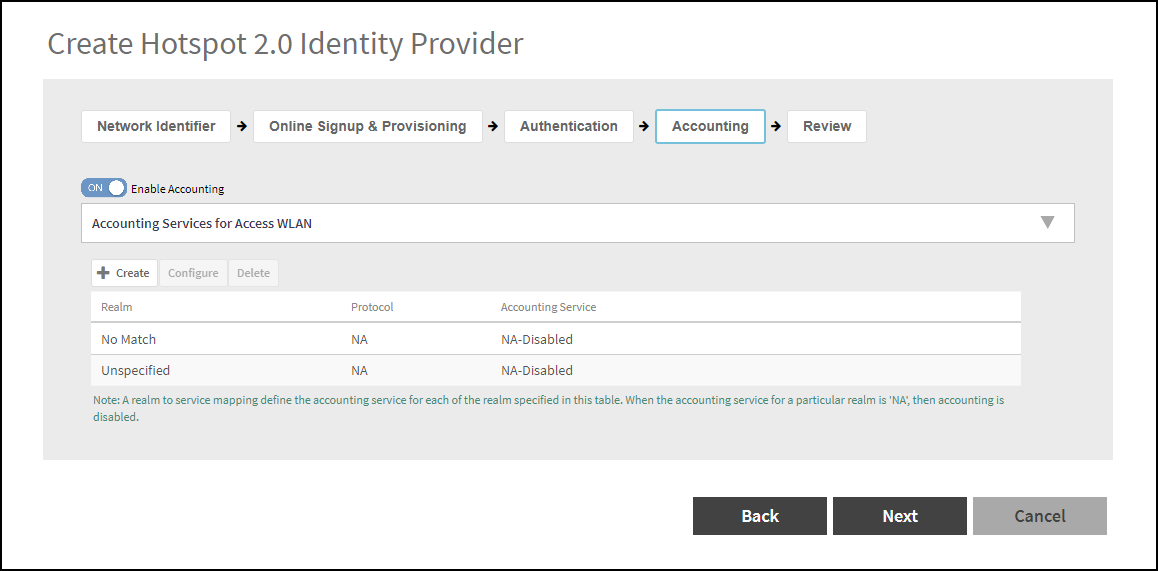
Accounting
- This feature is OFF by default, turn
it ON to enable accounting and to display the table.
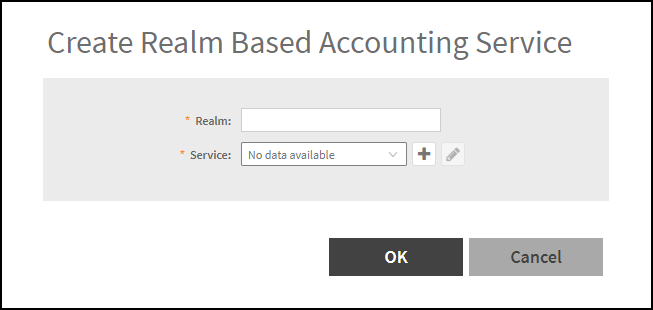
Click Create to display the Create Realm Based Accounting Service dialog box.
Complete the following fields:
- Realm: Enter the realm information.
If the authentication's realm is set as remote credential type, administrator should set this realm here to the customer's external accounting server.
- Service: Select the service from
the drop down list.
To create a realm service, click the
 icon to display the Create Accounting
Service dialog box. Create an authentication service, refer to Creating Proxy Accounting AAA Servers.
To modify the realm, select the realm from the table and click Configure Icon.
To delete the realm, select the realm from the table and click Delete Icon.
- Realm: Enter the realm information.
- Click Next.
 icon
to edit the selected realm service.