Creating Social Media Login Profile
When end-user associated with an OAuth 2.0
WLAN, launches his browser. AP redirects it to the OAuth 2.0 provider login page.
The
end-user should enter his account and password to authenticate with OAuth 2.0 provider.
AP
sets the end-user status as authenticated and user is able to use internet.
To configure social media authentication configuration, perform the following:
- Go to . This displays the zones associated with the Non-Proxy (Social Login).
- In the Non-Proxy (Social Login) screen, select a Zone and click Create.
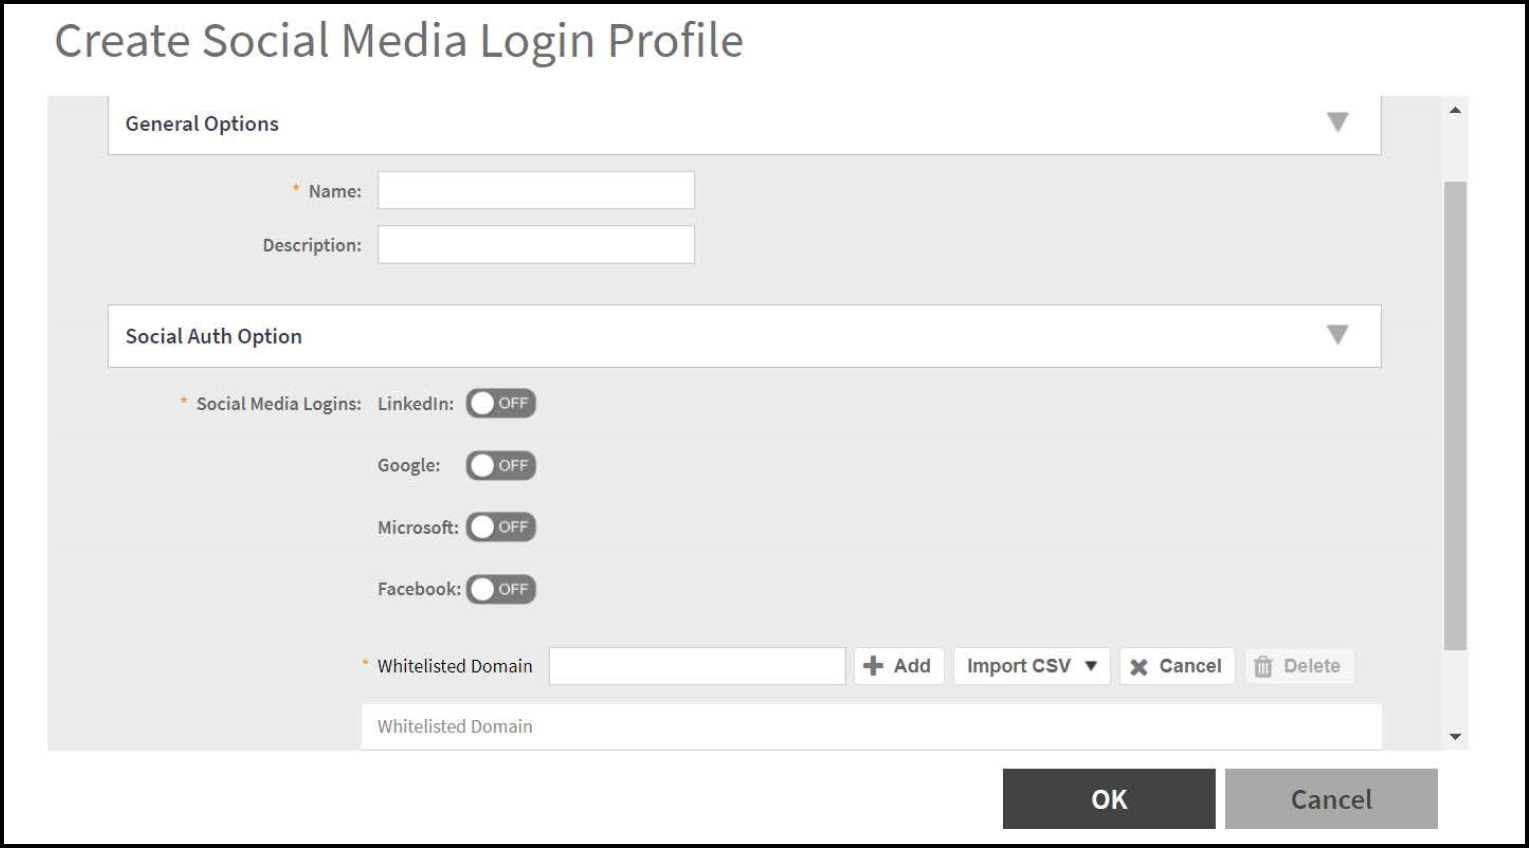
- Enter the values in General Options and enable the Social Auth Option tabs.
- After you have enabled the Social Media Logins it is mandatory to provide the client ID/Secret. If you don't have one, click on the hyperlink provided in Create Social Media Login Profile screen to generate a Client ID and Client Secret for particular social media website.
- Add domains to the Whitelisted Domain field by entering
the domain name. For example,
- LinkedIn - *.licdn.com, *.linkedin.com
- Google - *.geotrust.com, *.gstatic.com
- Facebook - *.facebook.com, *.fbcdn-profile-a.akamaihd.net, *.fstatic-a.akamaihd.net
- Microsoft - *.geotrust.com, *.live.com, *.microsoftonline.com, *.auth.gfx.ms, *.msauth.net
Note: Microsoft based Social media authentication do not support corporate accounts, but personnel email account.