MACsec over VXLAN
In this solution, a Media Access Control security (MACsec) session must be established over a VXLAN tunnel using an external loopback connection. For each MACsec session, from one site to another site there should be a dedicated port for the loopback connection and a dedicated VLAN that is mapped to the VNI. The VNI that is mapped to the dedicated VLAN is the cross-connect VNI which provides point-to-point Layer 2 extensions across the LAN/WAN. The external loopback port connected to the MACsec port must be the only member of the dedicated VLAN. The VLAN that is used for the cross-connect VNI cannot be used as a regular user VLAN, and any other VLAN-level feature must not be enabled. The protocol packets coming to the port which belong to the cross-connect VNI are not copied to the CPU. MAC learning is disabled on the port too. Any packets routed to the MACsec port will be encrypted and tunneled to the remote Virtual Tunnel End Point (VTEP). On the receive path, packets will be decrypted and forwarded.
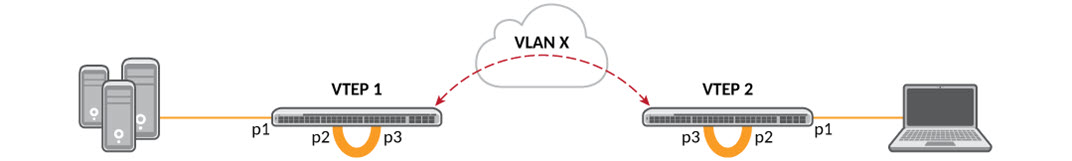
In the example in MACsec over VXLAN Packet Flow, port p1 is connected to the end user. Port p2 is the MACsec port, which has an external loopback connection to port p3. The traffic that enters the device on access port p1 is switched to MACsec port p2. At port p2, traffic is encrypted and sent out of port p2. Because there is an external loopback configuration, encrypted traffic is received on port p3, which is the only member of the dedicated VLAN. This VLAN is VLAN X. VLAN X is mapped to the VNI so that the encrypted traffic is VXLAN-tunneled to the other VTEP. When the traffic is received on the other VTEP, after VXLAN de-tunneling, the payload-encrypted Layer 2 frame is switched to port p3. Due to the external loopback, encrypted traffic is received back on port p2. At port p2, traffic is decrypted and switched to port p1.