Viewing Policy Information
The following table shows you an example of what a policy table looks like after three different policies have been created, and have been assigned to PEAP and/or DPSK pools.
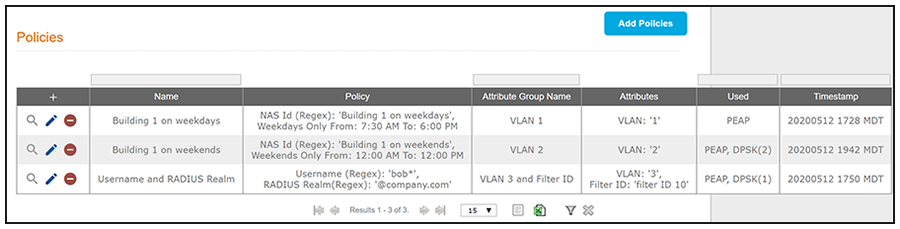
You can use the policy table as follows:
Description of Policy Table
| Column Title | Description |
|---|---|
| + |
|
| Name | The name of the policy as configured in the Display Name field in the Policy configuration screen, an example of which is shown in Create Policy Screen. |
| Policy | All the conditions that you set when you created the policy are listed in this column. For example, the "Building 1 on weekdays" policy conditions are the ones that were configured in the example shown in Create Policy Screen |
| Attribute Group Name | The name of the group that has been selected in the RADIUS Attribute Group drop-down when the policy was created. For the "Building 1 on weekdays" policy shown in this example, the group name VLAN 1 matches the selection that was shown in the example in Create Policy Screen. |
| Attributes | Lists all the attributes that were set for the corresponding RADIUS attribute group name. For the "VLAN 1" attribute group name shown in this example, the attribute "VLAN 1" is listed because that is the only attribute that was set during the configuration of the VLAN 1 RADIUS attribute group name, as shown in Create RADIUS Attribute Screen. |
| Used | Lists where a policy has been assigned as well as how many times it has been assigned for each category of authentication. For example, in the policy table example above, the policy called "Building 1 on weekends" has been assigned once to PEAP and twice to DPSK pools. |
| Timestamp | Time that the policy was created. |
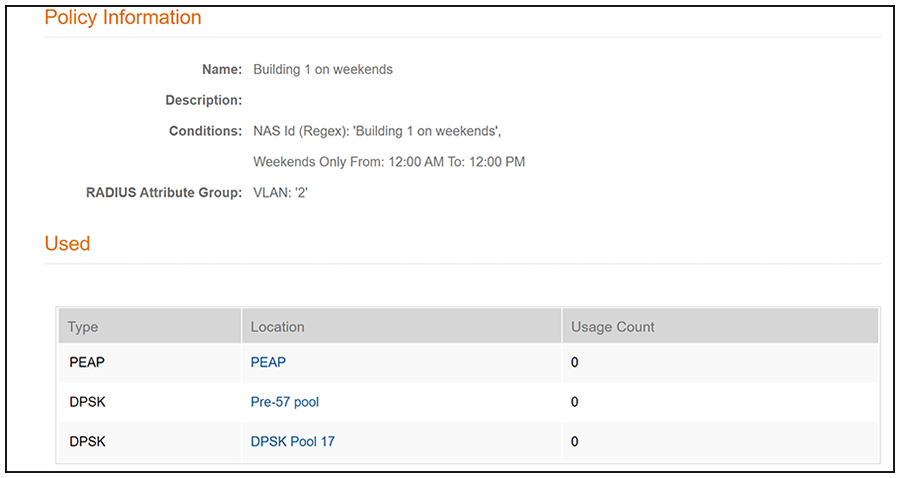
The screen above indicates that the policy is currently being used by PEAP and by two DPSK pools. The "Location" column of this screen in the UI provides live links to the specific configuration areas where the policy is used.
The Usage column will be incremented each time an enrolling user is assigned the policy in question. Also, If a device then gets assigned to a different policy and later gets reassigned to its original policy, the usage count of the original policy will be incremented.